Vulnerabilities, monthly patch compliance, hardware and firmware lifecycle, and framework compliance for cloud and on-premises, in one view, built from the tools you already run.
The demo runs on two fictional organisations with invented data. No sign-up; sample accounts are listed on the sign-in page.
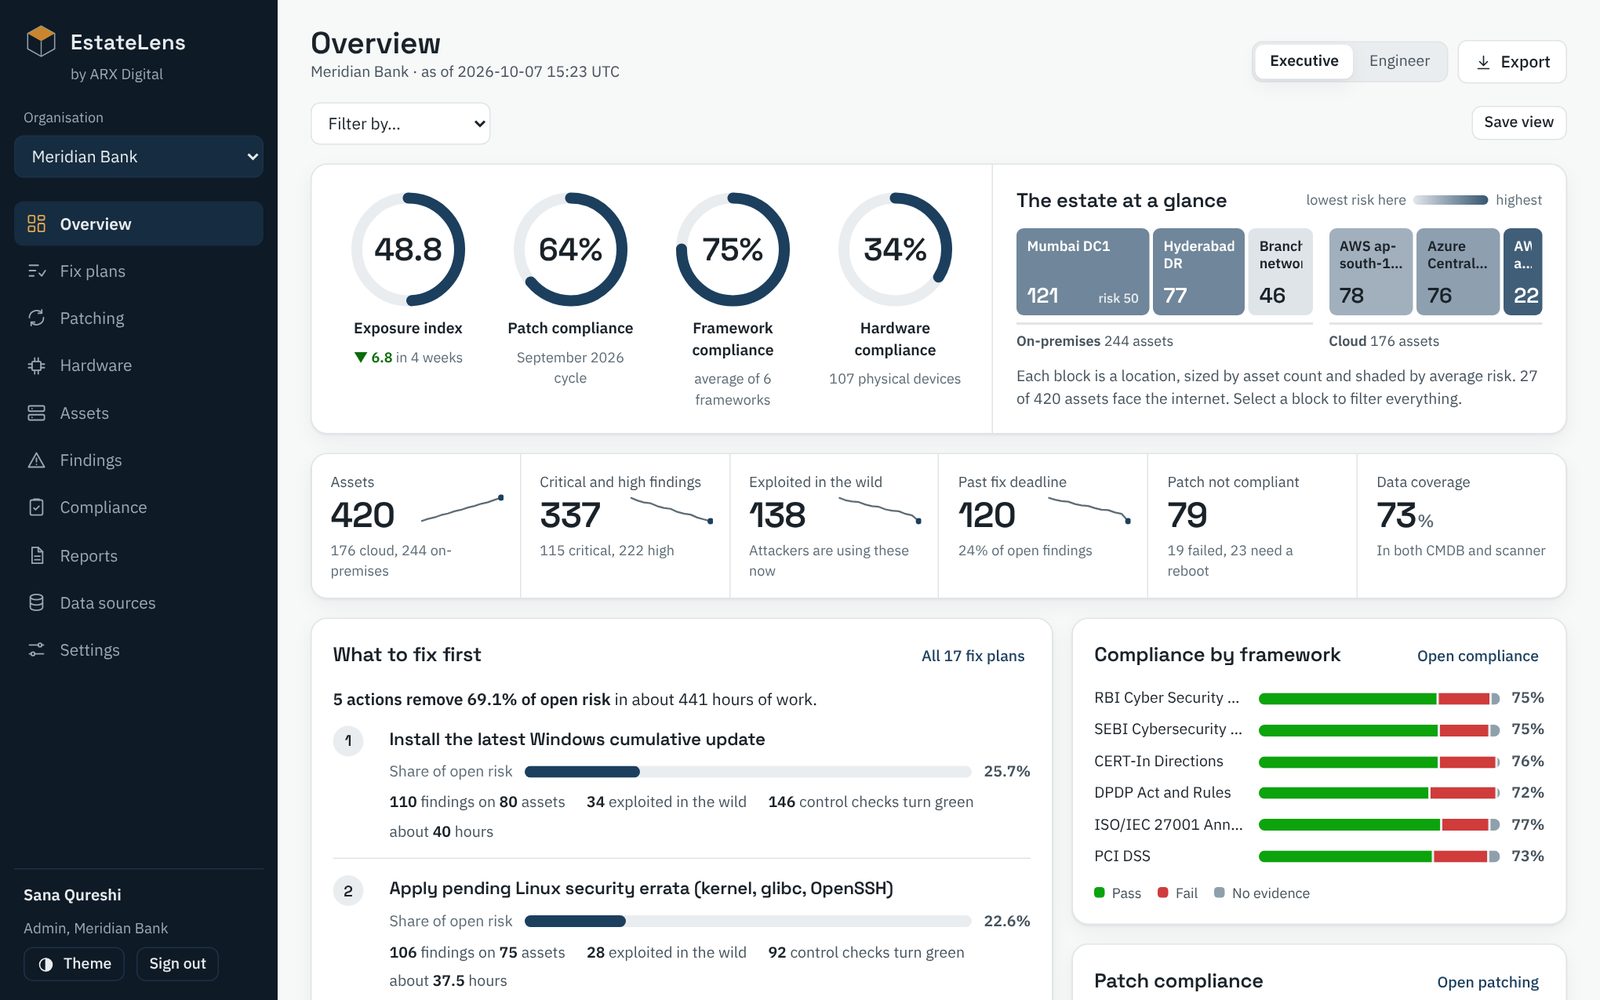
The CMDB, the scanner, the patch tool and the hardware console each describe a different estate. Leadership asks one question: are we exposed, and are we compliant? EstateLens reconciles the sources into one record per asset and answers from that.
Findings are grouped by the action that closes them and ranked by risk removed and controls turned green.
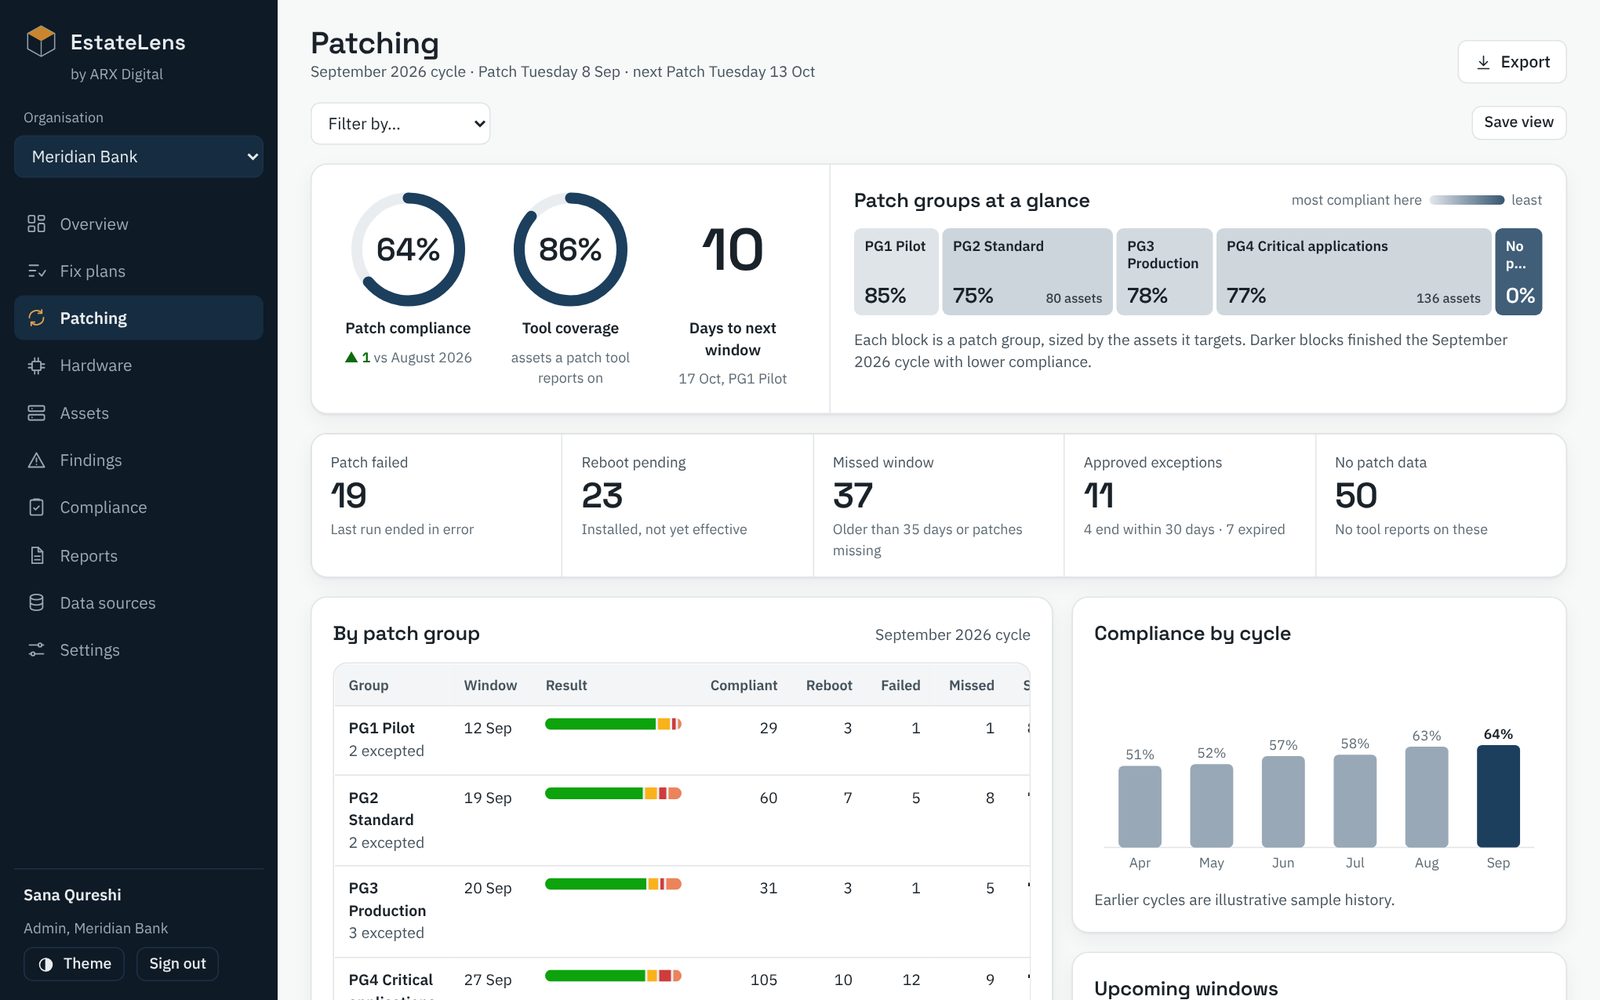
Compliant, reboot pending, failed, missed and excepted, by patch group, with the next window and what it should close.
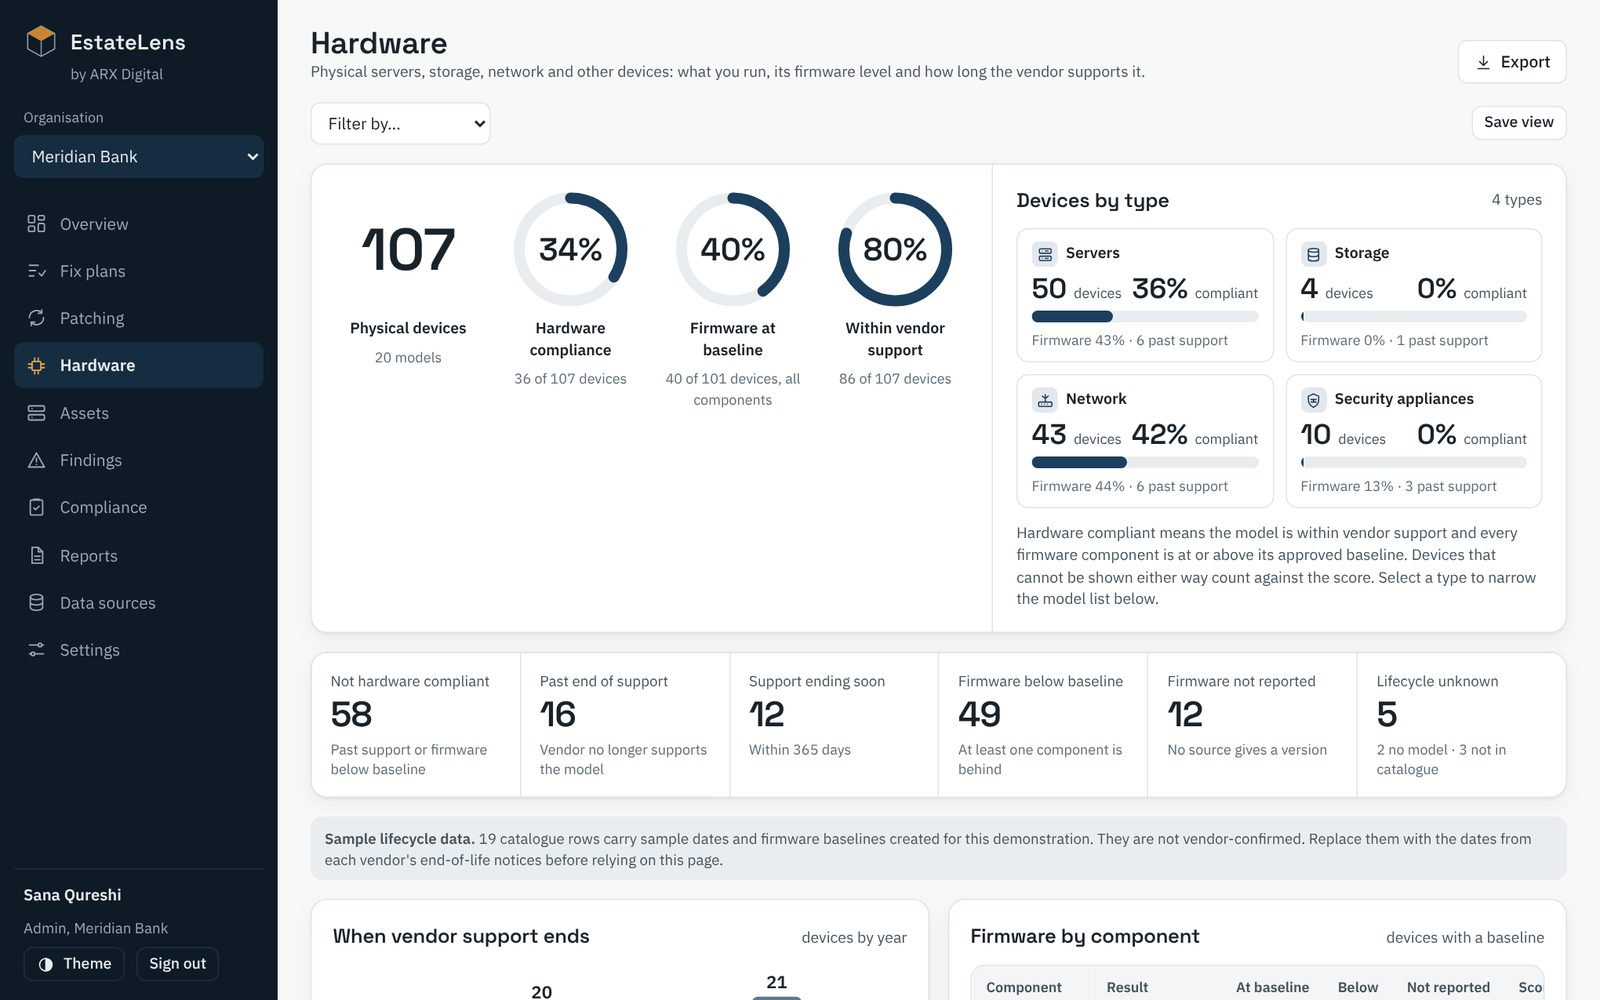
Physical servers, storage, network and security devices by model, firmware per component, and vendor support dates.
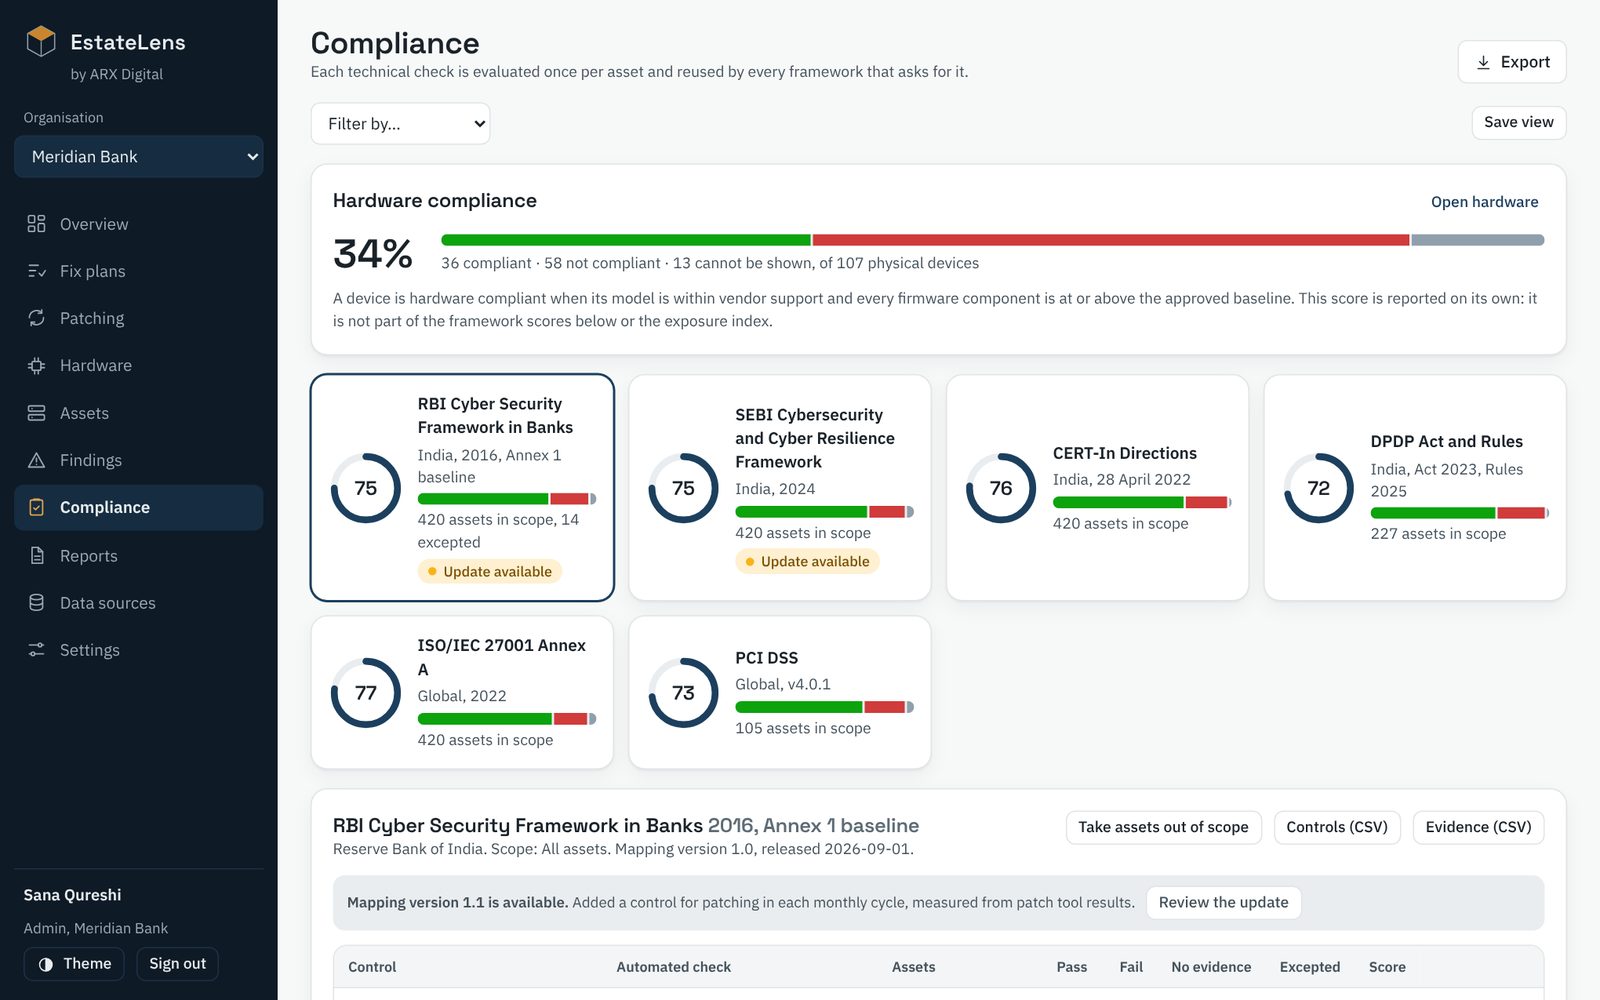
Each technical check runs once per asset and feeds every framework that asks for it, with exceptions kept out of the score and on the record.
Patch tools report success per job. EstateLens reports it per asset and per cycle, and counts an asset as compliant only when patches installed, nothing critical is missing and no reboot is pending.

A separate hardware compliance score: a device passes when its model is within vendor support and every firmware component is at or above your approved baseline.

Starter mappings for RBI Cyber Security Framework, SEBI CSCRF, CERT-In Directions, DPDP, ISO/IEC 27001, NIST CSF, CIS Controls, PCI DSS, GDPR Article 32 and HIPAA. Add your own framework from a spreadsheet.
The mappings cover asset-level technical controls and are a starting point. Have your assessor validate them before relying on them for an audit.

EstateLens is a working application in early access. This is what runs today and what is still being built.
Send three exports you already have. We load them into a private workspace and walk you through what they show.
Suited to banks, NBFCs, mid-size enterprises and the service providers who run their infrastructure.